A common misconception is that MEV protection is a switch a user turns on at the wallet level. In reality, it is a coordination problem between the wallet, the dApp, the blockchain’s transaction-ordering environment, and sometimes a specialized transaction relay. A wallet can warn you about a risky approval or simulate a swap, but it cannot automatically erase every information advantage available to validators, searchers, builders, or competing traders.
MEV, or maximal extractable value, describes the value gained by changing the order, inclusion, or composition of transactions beyond the ordinary block reward and fees. In a decentralized exchange, that may involve arbitrage, liquidation, or sandwich trading. Some MEV supports market efficiency: arbitrage can pull prices across venues back toward alignment. Other forms impose a cost on ordinary users, especially when a pending trade reveals enough information for another actor to trade immediately before and after it.
Two protection models: private submission and informed execution
There are two broad ways to reduce MEV exposure. The first is to limit who can see a transaction before it is included. Instead of sending a transaction directly to a public mempool, a wallet or dApp may route it through a private transaction path. The goal is straightforward: if a searcher cannot observe the trade in advance, it is harder to construct a sandwich around it.
Private submission is useful, but it is not magic. The transaction still has to reach a block producer or builder, and the user is relying on that infrastructure to handle the order honestly and reliably. A private route may also have different inclusion behavior, fee requirements, or failure modes from the public mempool. If the relay is unavailable, the transaction may be delayed or fall back to a public route, potentially changing the user’s exposure.
The second model is informed execution. Here, the user or wallet estimates what the transaction is expected to do before signing it. Simulation can reveal the expected token amounts, state changes, contract calls, approvals, and possible reverts. This does not necessarily hide the transaction from searchers. Instead, it helps the user avoid signing an action whose outcome is already unfavorable or whose contract behavior differs from the user’s intention.
That distinction is easy to miss: privacy reduces the information available to an adversary, while simulation improves the information available to the user. They address different points in the attack chain. The strongest workflow often combines both, but a user should not confuse a clear simulation result with guaranteed MEV resistance. A simulated swap can still face price movement, changing liquidity, transaction reordering, or a different block state at inclusion.
How dApp integration changes the security boundary
DeFi users often think of a wallet as the security boundary. In practice, the boundary is distributed. The dApp defines the transaction payload; the wallet displays and signs it; the smart contract interprets it; the network determines when it is included; and external actors may observe or react to it. A problem in any one layer can undermine the others.
Good dApp integration therefore means more than connecting a wallet with a standard browser interface. The application should present a transaction that the wallet can interpret, simulate, and display in a meaningful way. Clear contract identity, understandable token movements, approval scope, recipient information, and expected outcomes all matter. If a dApp obscures a call behind a generic contract interaction, the user may be asked to approve an action without understanding its economic effect.
This is particularly important with token approvals. An approval is not the swap itself; it grants a spender permission to move a token under specified conditions. Broad or unlimited approvals can reduce friction, but they enlarge the consequences of a compromised contract, malicious front end, or mistaken interaction. A wallet that flags unusual approvals and simulates downstream effects can make that risk more visible, although the user still has to evaluate whether the dApp deserves permission.
For US-based DeFi users, the operational context is also worth considering. Network congestion, gas-price volatility, changing liquidity, and multiple EVM chains can make a transaction behave differently from what a user expects. A wallet designed for Ethereum and EVM environments can reduce switching costs across networks, but convenience may encourage rapid signing. The safer habit is to treat each chain and contract interaction as a separate decision rather than assuming that a familiar interface implies familiar risk.
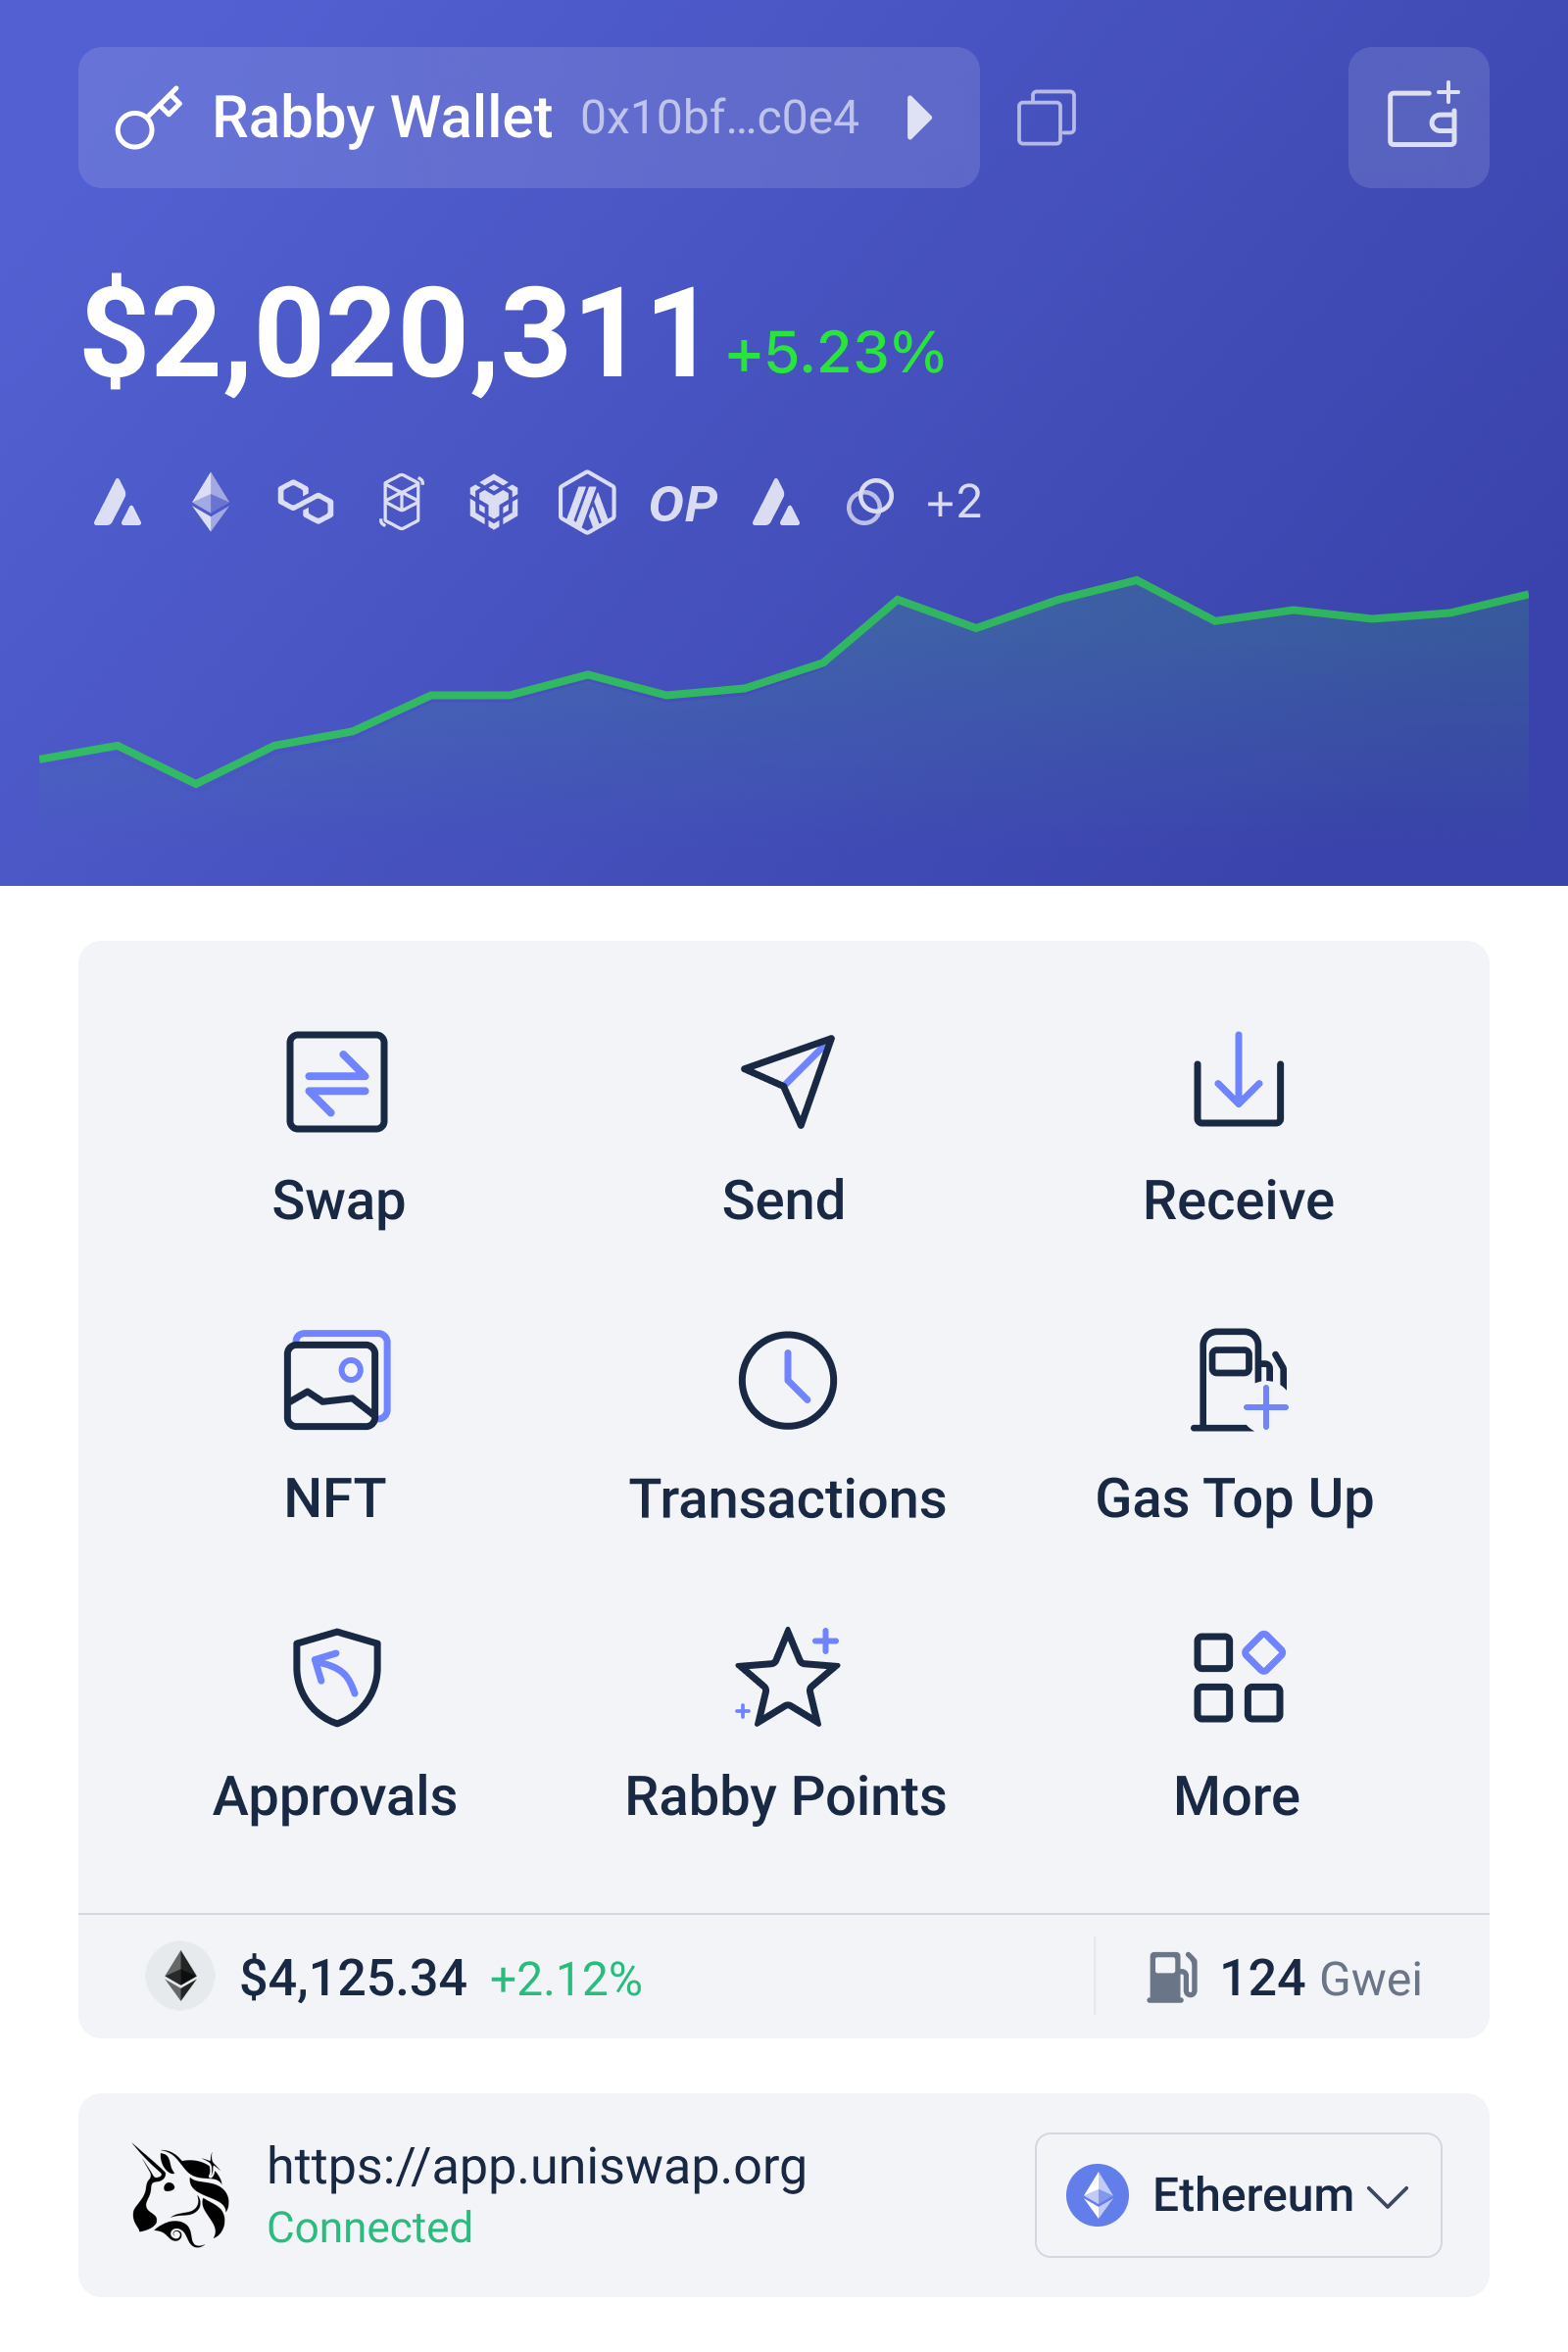
Rabby’s recent positioning as a wallet for Ethereum and EVM activity emphasizes broad chain access alongside security-oriented transaction review. For users assessing its role in a DeFi workflow, the practical question is not whether a wallet can promise perfect protection, but whether its checks improve the quality of decisions before signing. Exploring the wallet directly at https://rabby-wallet.at/ can be useful when comparing how transaction simulation, warnings, and dApp connectivity fit together in practice.
Comparing DeFi execution approaches
A public-mempool transaction is usually the simplest approach. It can be widely propagated and may be included quickly when the fee is competitive. Its weakness is visibility: pending transactions may expose trade size, route, slippage tolerance, and target pool. That information can be enough for automated strategies to compete for position around the transaction.
A private transaction route reduces that visibility. It may be preferable for larger swaps, sensitive rebalancing, or transactions with an obvious price impact. The trade-off is dependency. Users must trust the route’s availability and policies, and they may lose some transparency about how their transaction is propagated. Private submission can also protect the transaction’s path without solving a bad trade, an unsafe approval, or a malicious contract.
Limit orders, batch auctions, and intent-based systems take a different approach. Rather than asking the user to specify every low-level transaction detail, the user expresses a desired outcome, such as selling an asset above a given price. A solver or auction mechanism then attempts to execute that intent. This can reduce some forms of information leakage and competition over transaction ordering, but it introduces new questions: who selects the solver, how is execution quality measured, and what happens when the requested outcome cannot be met?
Direct interaction with an automated market maker remains flexible and composable, which explains its continued importance across DeFi protocols. Yet flexibility creates more parameters for the user to inspect: route, slippage, deadline, pool depth, fee tier, and token behavior. A warning system can identify suspicious patterns, but it cannot determine a user’s acceptable price impact or financial objective. Security tooling supports judgment; it does not replace it.
A practical risk framework for MEV-aware users
Before signing, separate three questions. First, is the contract interaction legitimate? Second, is the expected economic result acceptable? Third, is the transaction’s visibility likely to create an avoidable execution disadvantage? The first question is about authorization and code interaction. The second is about price, slippage, and liquidity. The third is about propagation and ordering. Treating these as separate questions prevents a reassuring simulation from being mistaken for a complete safety assessment.
For a small, liquid swap with modest slippage, public submission may be an acceptable convenience trade-off. For a large trade in a shallow pool, a private route, a lower-impact execution method, or a staged order may deserve consideration. If a transaction involves a new protocol, unfamiliar token, or broad approval, contract and permission review should take priority over speed. The right choice depends on exposure, not on a universal claim that one routing model is always safest.
One useful heuristic is to compare the value at risk with the information revealed. A small transaction may not justify complex execution infrastructure, while a transaction that can move a pool price or trigger a liquidation deserves more deliberate handling. Slippage settings should also be understood as economic permissions: a wide tolerance does not merely improve the chance of execution; it permits a worse outcome if market conditions or ordering change.
What to watch as DeFi infrastructure develops
The next phase of MEV protection is likely to be shaped by integration rather than by a single feature. Wallets, dApps, wallets’ simulation engines, private relays, and protocol-level auction designs may increasingly work together. If that happens, users could receive more context about both contract behavior and expected execution conditions before signing. The important signal will be whether these systems expose assumptions clearly rather than hiding complexity behind a reassuring label.
Several uncertainties remain. Simulations depend on a particular state snapshot, and the blockchain may change before inclusion. Private routes can reduce public visibility but create infrastructure dependencies. Solver-based execution may improve outcomes in some markets while concentrating discretion in fewer intermediaries. These are not reasons to reject the tools; they are reasons to evaluate what each tool protects, what it assumes, and what failure looks like.
Frequently asked questions
Does transaction simulation prevent sandwich attacks?
No. Simulation helps estimate the transaction’s result and can expose suspicious calls, unexpected token movements, or likely slippage. It does not by itself hide a pending transaction or control its ordering. Private submission and suitable execution design address that separate problem.
Is private transaction submission always safer than using the public mempool?
Not always. It can reduce exposure to public observation and therefore lower the opportunity for some sandwich strategies. However, it introduces reliance on private infrastructure and does not make an unsafe contract safe, guarantee inclusion, or ensure a favorable price. The appropriate choice depends on transaction size, liquidity, urgency, and the reliability of the route.
What should a DeFi wallet show before I sign?
At minimum, inspect the destination contract, requested approvals, tokens entering and leaving your wallet, estimated amounts, slippage or minimum received, network, gas cost, and any unusual permission. When the wallet can simulate the call, compare the simulation with the dApp’s stated purpose. A mismatch is a reason to pause, not merely click through a warning.
MEV protection is best understood as risk management across an execution pipeline. A wallet can improve visibility, a dApp can provide cleaner transaction context, and a private route can reduce information leakage. None is sufficient alone. The sharper question is not “Am I protected?” but “Which part of this transaction is protected, under which assumptions, and what remains exposed?”
 We serve the entire Phoenix area, including
 We accept Cash, Checks and Major Credit Cards.